Flibo
Private Local-First Reconnaissance & Attack Surface Mapper
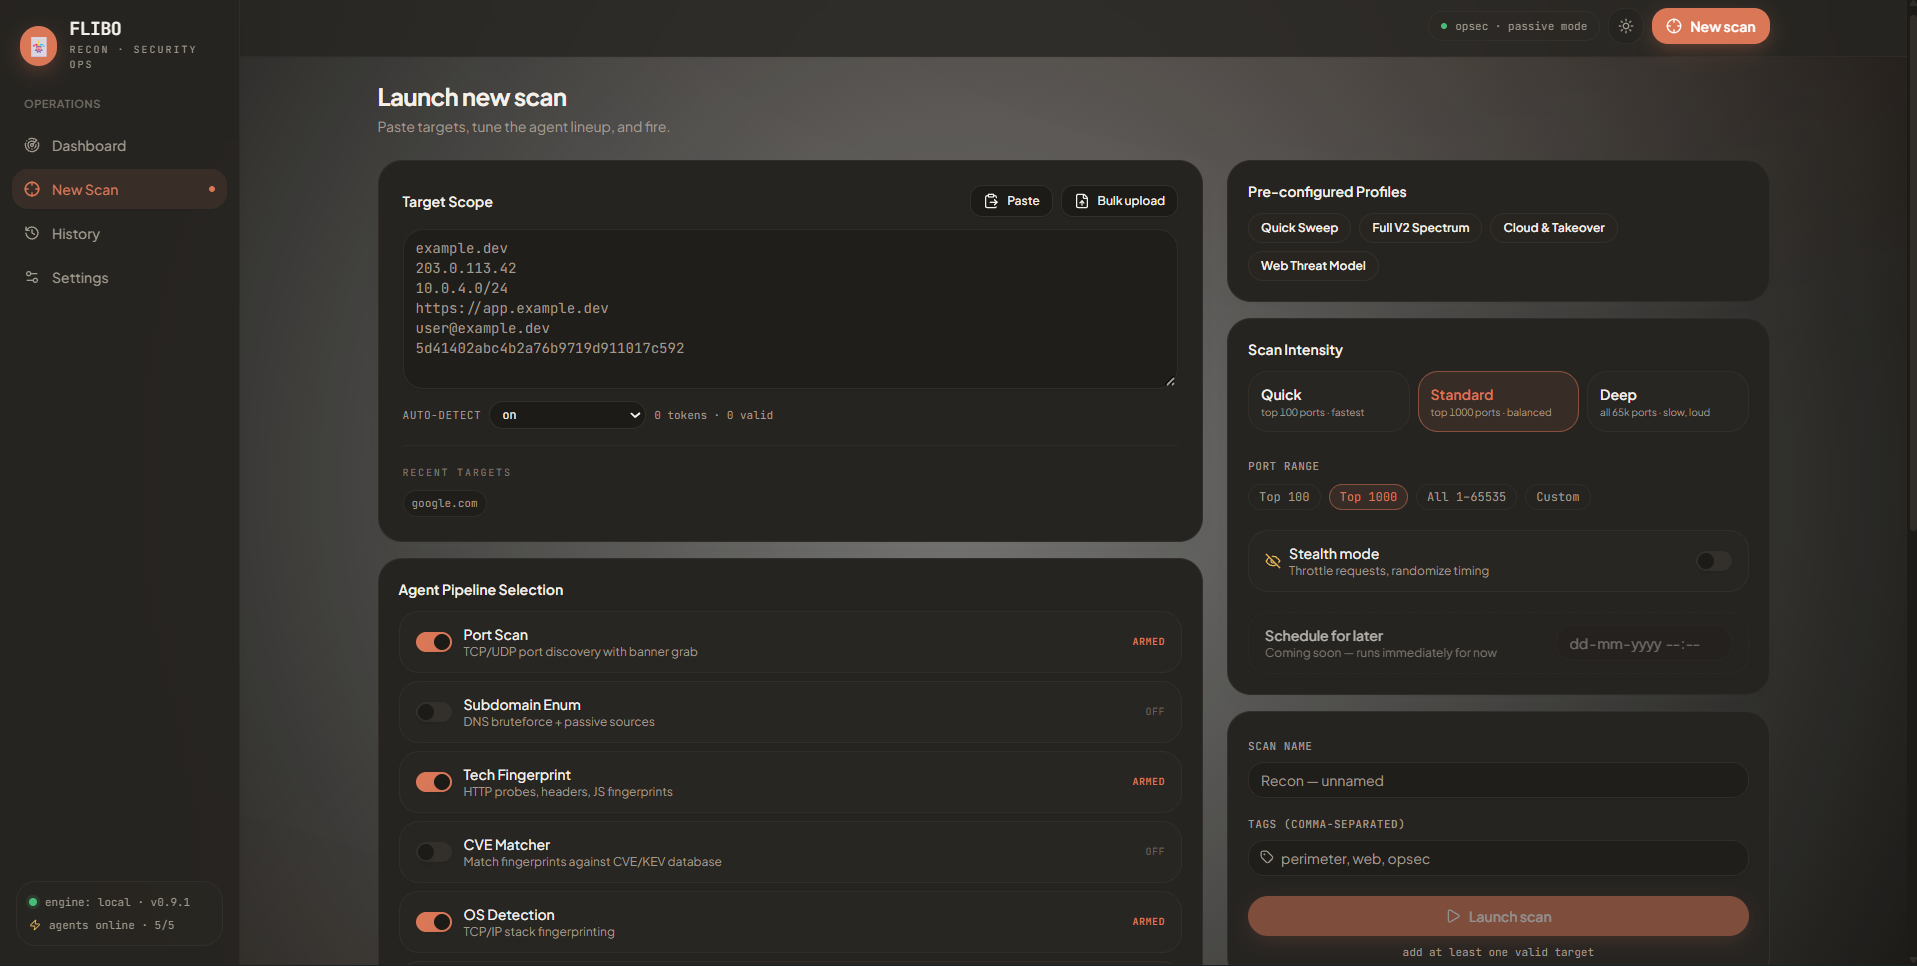
Private, local-first reconnaissance automation and attack surface mapping console bridging raw socket-level network reconnaissance with CVSS 3.1 vulnerability correlation.
Why Air-Gapped Reconnaissance Matters
Offensive security operators, red teamers, and penetration testers regularly perform external and internal reconnaissance. However, standard SaaS-based attack surface management platforms demand that organizations stream internal IP ranges, domain lists, and vulnerable service signatures into third-party cloud databases.
Conversely, raw CLI tools like Nmap, amass, and sublist3r dump voluminous, disconnected text files that require manual scripting to correlate with CVE databases or synthesize into coherent attack paths.
Flibo bridges this divide. It delivers an editorial operator console styled with Claude's signature warm terracotta palette, backed by a native Node.js socket engine that executes real network reconnaissance, streams terminal events live via SSE, and correlates CVSS 3.1 attack chains completely locally on disk.
Capabilities & Architectural Innovations
Native Node.js Socket Engine
Executes real TCP socket connects, DNS record audits, Certificate Transparency queries, HTTP/TLS fingerprinting, and service banner inspection without external wrappers.
Real-Time Telemetry Pipeline via SSE
Streams terminal stdout, agent transitions, and discovered findings instantaneously using Server-Sent Events (/api/scans/:id/events) with zero polling overhead.
Automated Multi-Target Perimeter Classifier
Instantly detects and normalizes inputs across IPv4 quads, CIDR subnets, Fully Qualified Domain Names (FQDNs), URLs, and artifact hashes.
Automated Attack-Chain Synthesis & CVSS 3.1
Correlates open ports and banner fingerprints against local CVE dictionaries, prioritizing risks into Critical (Warm Vermilion), High (Sunset Orange), Medium (Golden Ocher), and Low (Sage).
Offline-Resilient Dual Runtime
Seamlessly falls back to autonomous client-side simulation workers when running in fully disconnected air-gapped environments without raising runtime exceptions.
Executive & Technical Multi-Format Export
Produces raw JSON, tabular CSV with CVSS scores, structured Markdown executive summaries, and CSS print-styled white PDF reports.
Reconnaissance & Synthesis Workflow
From raw IP entry to interactive attack-chain graph, Flibo conducts automated reconnaissance sweeps across structured parallel agents.
Target Classification & Scope Definition
Operator inputs target specifications. Flibo's regex classifier validates domains, CIDRs, and IPs, dynamically assembling the optimal agent lineup.
Concurrent Socket Probing & DNS Auditing
Parallel workers execute TCP connects across top port ranges, extract TLS certificate metadata, and harvest DNS records (A, AAAA, MX, TXT, SOA).
HTTP Fingerprinting & Banner Extraction
Probes web endpoints for server headers, SSL/TLS ciphers, technology stacks, and hidden security misconfigurations.
CVSS Vulnerability Correlation
Discovered services and versions are queried against local vulnerability catalogs to identify exploitable attack paths and CVE impact scores.
Live SSE Broadcast & Attack-Chain Graph
Findings stream into the operator console in real time, rendering an interactive relationship graph of vulnerable network perimeters.
Artifact Analysis & Screenshots
Click any image to inspect forensic details, telemetry graphs, and terminal outputs at high resolution.
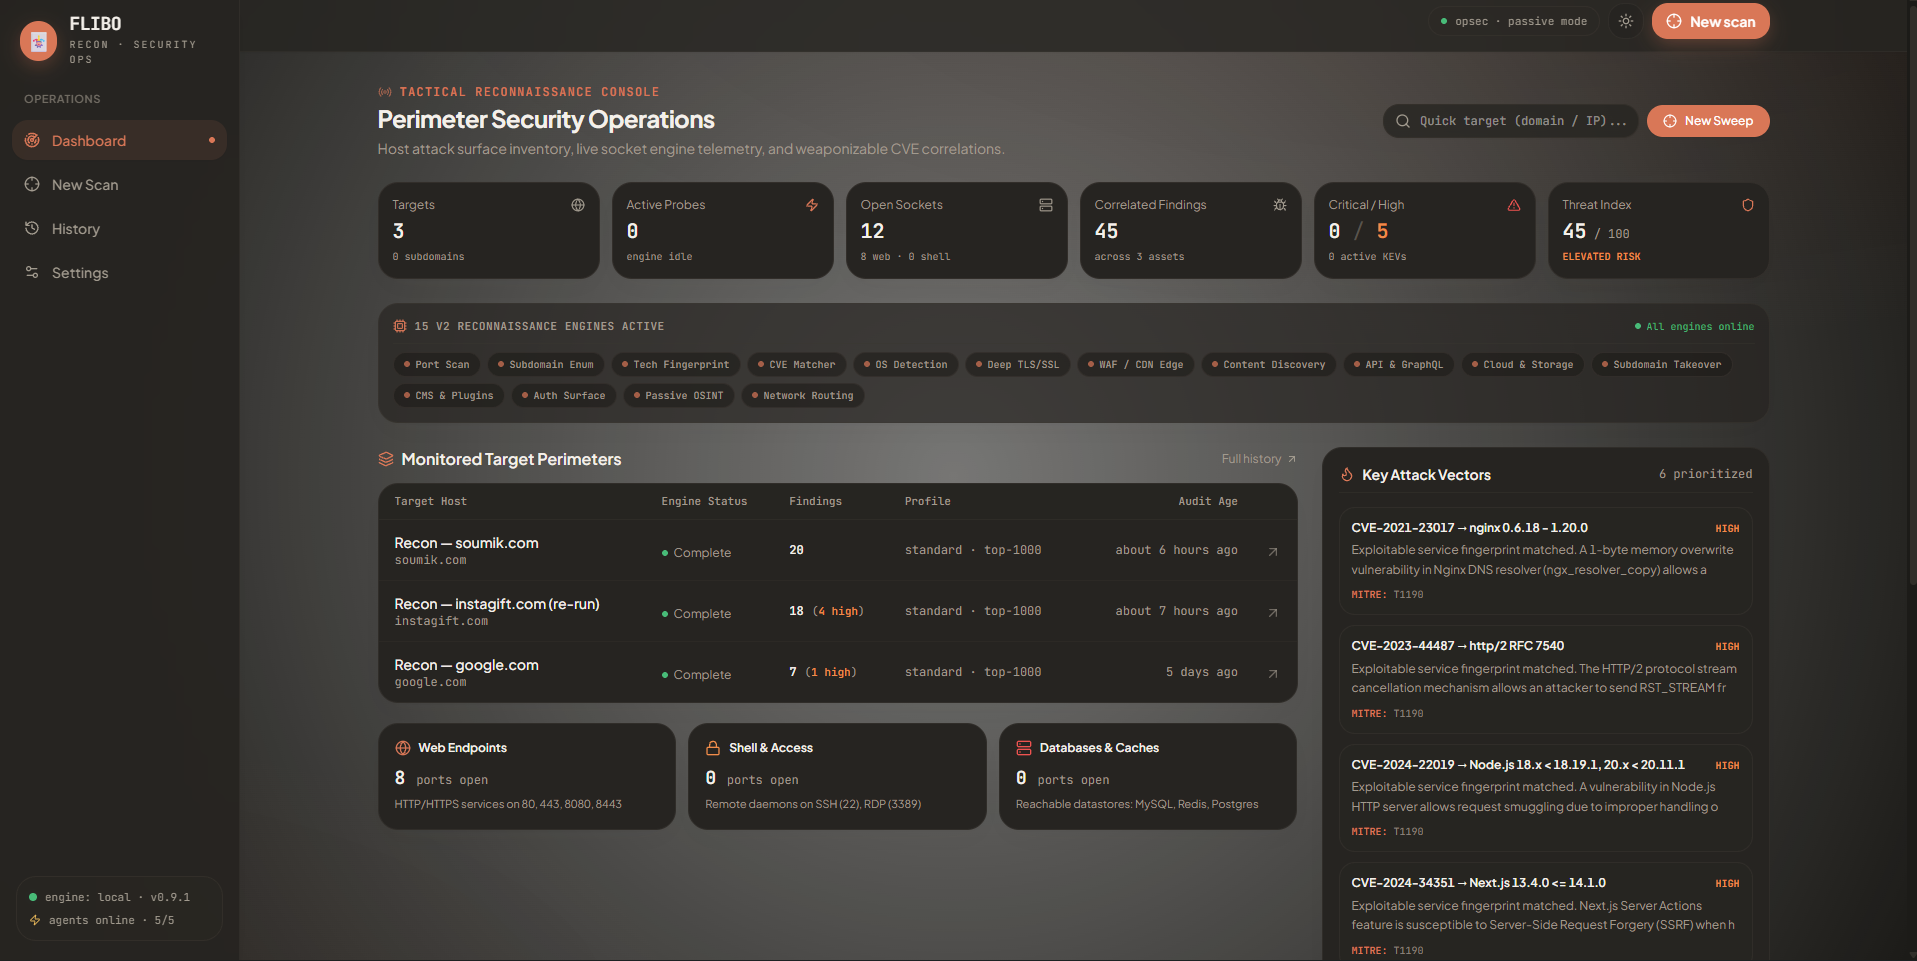
Flibo Operator Console Overview
Perimeter Dashboard & Attack Vector Severity BreakdownThe main Flibo reconnaissance console displaying target perimeters, high-level severity distribution, active scans, and perimeter telemetry metrics.
Scan Detail & Real-Time SSE Terminal
Live EventSource Stream & Discovered Findings LogThe granular scan detail view featuring the embedded LogConsole terminal with live TCP probe stdout, running agent state indicators, and real-time CVE findings.
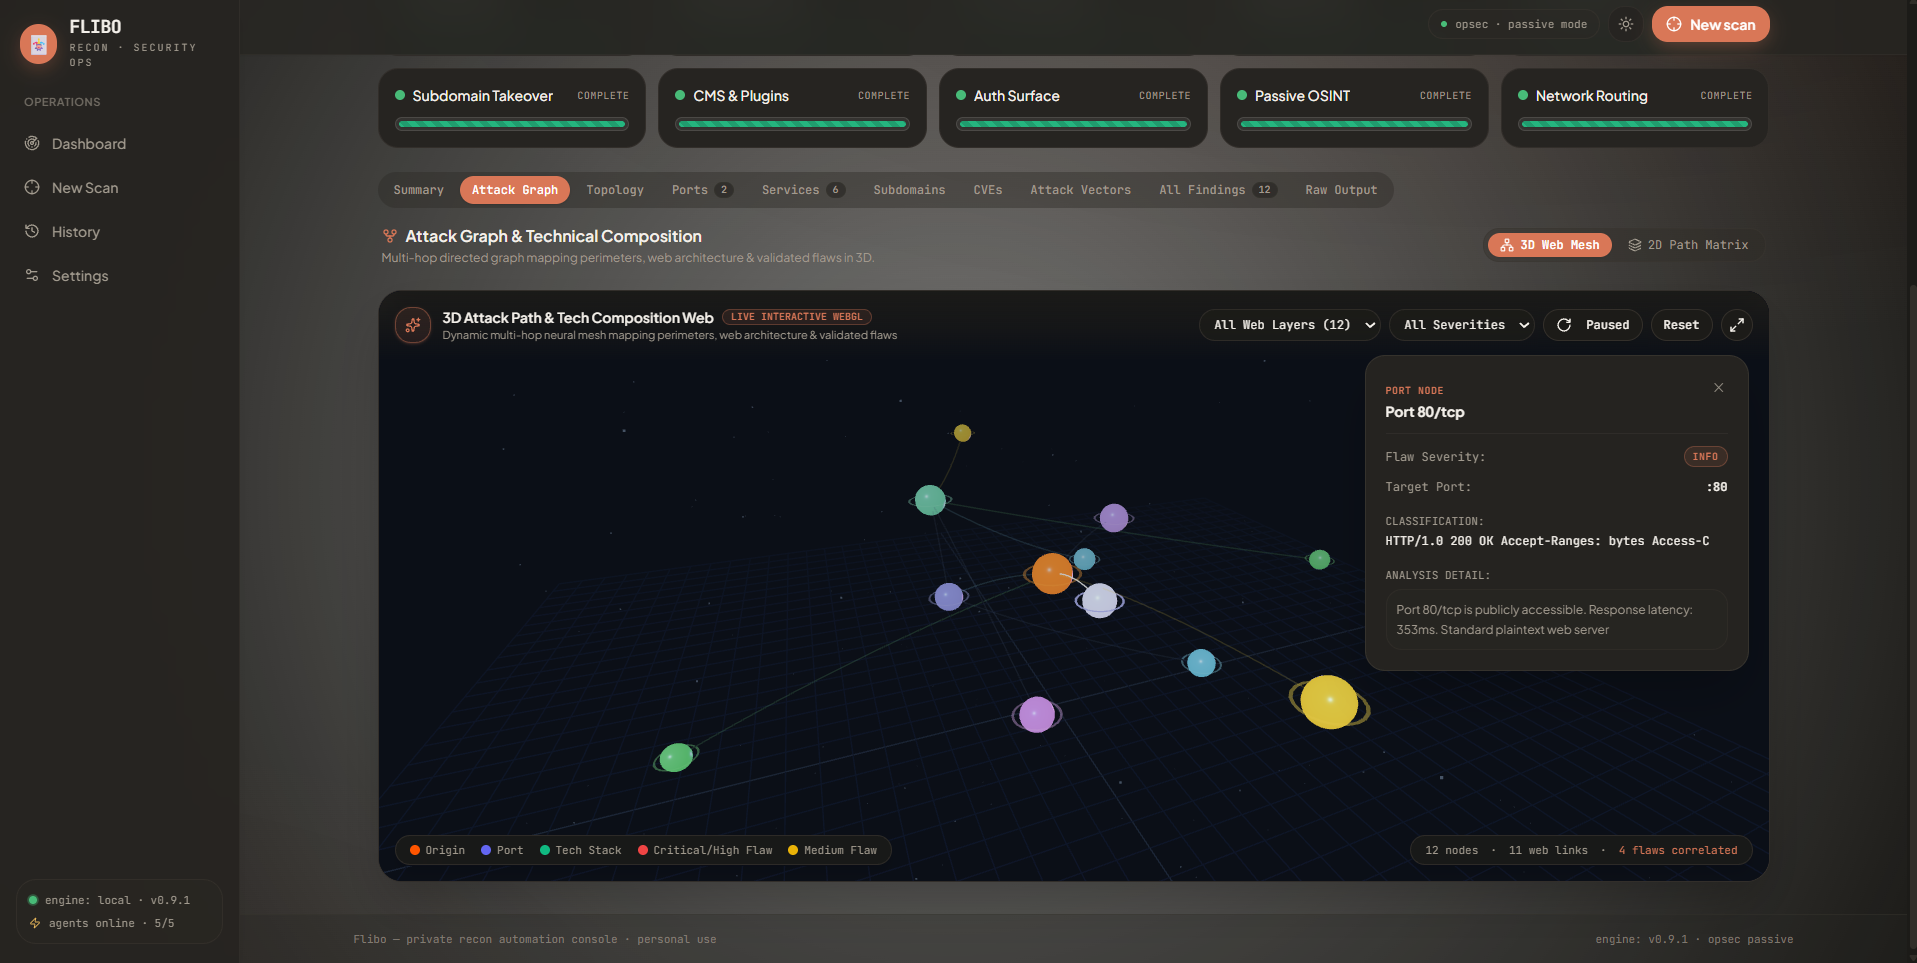
Interactive Attack Surface & Service Topology
Visual Network Graph & Exposure VectorsSpatial service map demonstrating relationships between open ports, exposed protocols, and correlated exploit vectors across scanned subnets.
Zero Cloud Dependencies
All databases, CVE catalogs, and scan states persist strictly to local disk.
Editorial Claude Aesthetic
Warm terracotta (#D97757) accents, warm ivory light mode, and carbon dark mode.
Interactive Findings Table
Instant sorting by CVSS score, port, service name, and remediation priority.
Print-Optimized White PDF
Specialized CSS @media print layout for crisp executive deliverables.